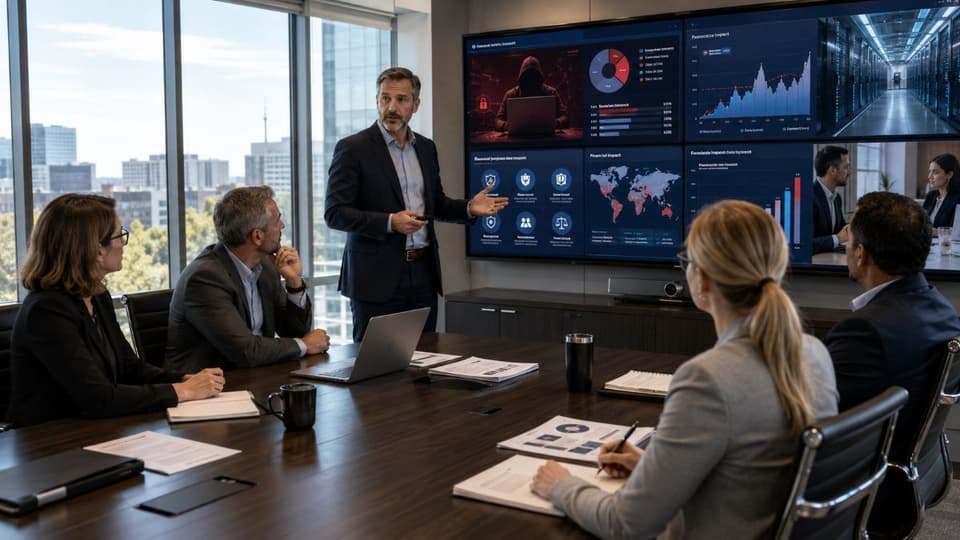
Cyber insurance covers two kinds of loss. First-party coverage pays your own costs after an attack: forensic investigators, legal advice on who you must notify, data recovery, lost income, extortion and some fraud. Third-party coverage pays when customers, partners or regulators say your security failure harmed them. Exclusions, sublimits and retentions then decide how much of either you actually collect.
That split comes straight from regulators. The NAIC cyber insurance guide for small businesses, written with the FTC, tells owners to decide with their agent whether they need first-party coverage, third-party coverage, or both. This guide walks through what each side pays for, the exclusions that cause the most claim disputes, and the policy terms that shrink a payout. If you want the other half of the picture, the security controls an underwriter checks before quoting, read our guide to cyber insurance requirements.
What cyber insurance coverage is, and why your other policies fall short
Cyber insurance is a policy built for the financial fallout of a data breach, a network attack or online fraud. General liability and property policies are written around bodily injury and physical damage. A ransomware lockout or a stolen customer list is neither, so those policies often respond poorly or not at all. Read your current policies for data and electronic records exclusions before you assume you are covered.
The market is large and still settling. The NAIC 2025 report on the cybersecurity insurance market puts United States direct written premium at about $9.14 billion for 2024, a 7% drop from 2023 and the first decline on record. Claims rose almost 40% to nearly 50,000. The same report shows how cyber cover is sold. Endorsements added to another policy make up 55.1% of policies in force but only 4% of premium. In plain terms, many businesses hold a small cyber add-on, not a full standalone policy. If your cyber cover arrived as a line on a package policy, check its limits first.
First-party vs third-party cyber coverage: what each pays for
First-party coverage pays your business directly for its own losses. Third-party coverage, often called cyber liability, pays to defend and settle claims that other people bring against you. The table uses the coverage lists in the FTC cyber insurance guidance and adds a plain example for each line.
| Coverage | Side | What it pays for | Plain example |
|---|---|---|---|
| Forensics and incident response | First party | Investigators who find how attackers got in, contain them and confirm what data was touched | A bookkeeper's laptop shows signs of remote control and you need to know if client files left the building |
| Breach legal counsel | First party | Lawyers who work out your notification and regulatory duties | Deciding which states' notice laws apply to a stolen spreadsheet |
| Notification and call center | First party | Letters to affected people, a call center and credit monitoring | Mailing 2,000 patients and staffing a hotline for questions |
| Data and system recovery | First party | Recovering or replacing lost or stolen data and rebuilding systems | Restoring a file server after ransomware encrypts it |
| Business interruption | First party | Income lost while systems are down, usually after a waiting period | A clinic cannot book appointments for three days |
| Cyber extortion | First party | Negotiators and, where legal, a ransom payment | Criminals threaten to publish client records unless paid |
| Crisis management | First party | Public relations help after an incident | Preparing a statement before the local news calls |
| Privacy liability | Third party | Payments to affected consumers, settlements, damages and judgments | Customers sue after their card numbers are stolen from your site |
| Regulatory defense | Third party | Costs of litigation and responding to regulatory inquiries | A state attorney general asks for your security records after a breach |
| Media liability | Third party | Claims for defamation and copyright or trademark infringement | A photographer claims your website used an image without a license |
First-party coverage in practice
First-party costs land in the first hours and days. You pay a forensic firm to stop the attack, a breach lawyer to decide what you owe the public, and staff overtime to rebuild. Revenue stops while the phones and the scheduling system are dark. The FTC list also includes cyber extortion and fraud, plus fees, fines and penalties tied to the incident, though each of those usually has its own limit, as covered below.
Third-party coverage, also called cyber liability
Third-party coverage responds when someone else makes a claim. Cyber liability is often written on a claims-made basis, so the claim must be first made during the policy period. The Travelers and AXIS applications linked in this guide both say so. Read two things closely. First, the FTC suggests looking for "duty to defend" wording, which means the insurer runs and pays for your defense. Second, check whether defense costs sit inside the limit. A Travelers CyberRisk application warns that the limit "may be completely exhausted" by defense costs. A long lawsuit can use up the money meant for a settlement.
Common cyber insurance exclusions and what they mean for a claim
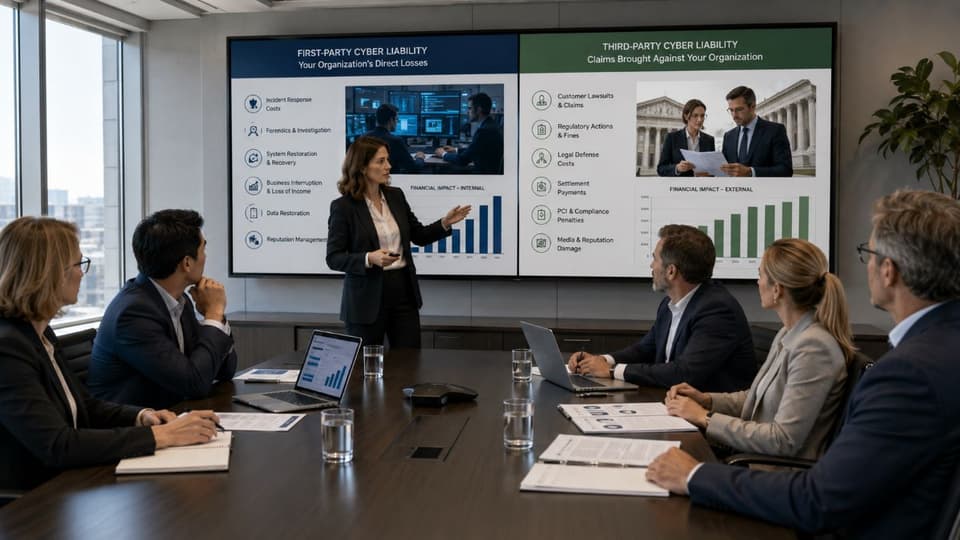
Cyber policies are not standardized, so every exclusion depends on the exact wording. A published specimen helps show how the clauses read. The examples below quote a Chubb Cyber Enterprise Risk Management specimen wording from 2019 (a Singapore edition). Your policy will differ, but the same families of exclusions show up across the market.
War and state-backed cyber attacks
Most policies exclude war, and many now exclude attacks backed by a government even when no shooting war exists. Lloyd's of London made this a market rule. Lloyd's Market Bulletin Y5381, dated 17 August 2022, requires standalone cyber policies written at Lloyd's to exclude state-backed attacks that significantly impair a state's ability to function or its security capabilities. It applies from 31 March 2023 at inception or renewal. The clause must also say how an attack will be attributed to a state and whether systems outside the affected state are excluded. Ask your broker which clause your policy uses and who decides attribution. The Chubb specimen excludes war but carves back "Cyber-Terrorism", which shows how much the details matter.
Prior acts, prior knowledge and retroactive dates
A policy only covers events inside its time window. A retroactive date is the earliest date a covered act can occur. If attackers broke in before that date, a breach discovered later can fall outside cover. A prior knowledge exclusion goes further. The Chubb wording excludes a wrongful act committed before the policy began if someone in management "knew or reasonably could have foreseen" it could lead to a loss. Applications ask about this directly. The Travelers form asks whether anyone is aware of any circumstance that could lead to a claim. Picture a firm that buys a policy in January, then learns in March that an intruder has sat in its email since November. That claim may fail on either clause.
Failure to maintain security and unpatched systems
Insurers price your policy on the controls you describe. If those controls lapse, coverage can lapse with them. A Reed Smith review of common cyber exclusions puts it simply: "Failing to maintain adequate security measures can make insurers refuse coverage." Some applications ask for patching speed in days, and the answers become part of the contract. An AXIS ransomware supplemental application asks for your critical patching target and states that the application "will form a part of the policy". A server left unpatched for months, after you said patches go in within a week, is exactly the gap a claims adjuster looks for.
Social engineering and funds transfer fraud sublimits
Wire fraud is a common coverage surprise. The FBI's 2024 IC3 Internet Crime Report counted 21,442 business email compromise complaints with reported losses of $2,770,151,146. Insurers treat these losses carefully because an employee usually sends the money willingly. The Travelers application lists social engineering fraud and funds transfer fraud as separate insuring agreements, each with its own requested limit and retention. That often means a policy with a $1 million headline limit pays far less for a fake invoice. If an employee wires $50,000 after a spoofed vendor email, the answer depends entirely on that line. Our guide to business email compromise covers the payment checks that stop most of these losses.
Betterment
Cyber policies restore you to where you were, not to something better. Upgrades during recovery are called betterment, and they are often excluded or sold as an extension. The Chubb specimen defines betterment costs as replacing software "with newer, upgraded and/or improved versions" and pays them only inside the data recovery limit, so every dollar spent on upgrades reduces what is left for restoration. If your recovery plan assumes you will replace an old server with a current one after an attack, ask whether that upgrade is covered.
Bodily injury and property damage
Cyber policies generally exclude bodily injury and damage to physical property, and leave those to your general liability and property policies. The Chubb specimen excludes any claim arising from bodily injury or property damage. Reed Smith notes the same exclusion often reaches damaged hardware, though some insurers sell "bricking" cover for devices made useless by corrupted software or firmware.
Contractual liability
Liability you take on by contract is usually excluded unless you would owe it anyway. The Chubb wording excludes claims for breach of contract, warranties and liquidated damages, then gives back three things: liability you would have without the contract, indemnities to clients about keeping their customers' data confidential, and payment card losses. Many client contracts now include security indemnities. Compare them with this clause before you sign, because a promise your policy will not back is a promise you fund yourself.
Infrastructure outages
Power, internet and utility failures that you do not control are usually excluded. The Chubb specimen excludes outages of electricity, gas, water and telecommunications, except systems under your own operational control that fail because of an attack. Some policies add cover for outages at your cloud or IT providers, so ask about dependent business interruption if your business runs on hosted software.
How sublimits, retentions, waiting periods and coinsurance shrink a payout
The headline limit is the most a policy will pay in total. Four other terms decide what you receive for a specific loss. The Chubb specimen schedule shows the structure clearly: one policy aggregate, separate limits per coverage, sublimits for regulatory fines, payment card loss and consumer redress, and a business interruption waiting period counted in hours. Corvus, a cyber insurer, explains sublimits and coinsurance and reported in January 2022 that AIG had introduced 50% ransomware coinsurance across its accounts.
| Term | What it means | What to check |
|---|---|---|
| Aggregate limit | The most the policy pays for all claims in the policy period | Whether defense costs reduce it |
| Sublimit | A smaller cap for one type of loss, carved out of the aggregate, not added to it | Ransomware, social engineering, regulatory fines, payment card loss |
| Retention | The amount you pay first on each claim, like a deductible | Whether different coverages carry different retentions |
| Waiting period | Hours of downtime before business interruption cover starts | Whether lost income during those hours is excluded |
| Coinsurance | A share of every covered loss that you pay, such as 50% | Which coverages it applies to and whether it is negotiable |
Here is a simple illustration with sample numbers. Say you hold a $1 million policy with a $250,000 ransomware sublimit, a $25,000 retention and 50% ransomware coinsurance. A ransomware incident costs $400,000. You pay the first $25,000. Coinsurance splits the remaining $375,000, so the insurer pays $187,500 and you pay another $187,500. Your $1 million policy covered less than half the loss. Policies apply these terms in different orders, so ask your broker to run your own numbers on a realistic incident.
Ransomware coverage: what insurers will and will not pay
Extortion coverage can pay negotiators and a ransom, but only where paying is legal. The Chubb wording covers extortion payments "where legally allowed and insurable". The Treasury Department's OFAC advisory on ransomware payments, updated 21 September 2021, warns that paying a sanctioned group can violate sanctions rules, names cyber insurance firms among those at risk, and says OFAC may impose civil penalties on a strict liability basis. It also treats prompt reporting to law enforcement as a significant mitigating factor. Read your policy's consent conditions before anything is paid.
The ransom is rarely the biggest cost. IC3 received 3,156 ransomware complaints in 2024 with $12,473,156 in reported losses, and the FBI notes that figure excludes lost business, time, wages, files, equipment and remediation services. Downtime and rebuilding are where most of the money goes, so business interruption and data recovery limits matter as much as the extortion line. Clean, tested backups through data backup and disaster recovery are what let you restore instead of pay.
Your policy also shapes the first hour. Many policies set notice deadlines and require the insurer's consent before you settle or hire certain vendors. Write the hotline number into the steps you follow in a ransomware attack so nobody wipes evidence or hires an outside vendor the insurer will not reimburse.
Are regulatory fines covered? Only where the law allows it
Regulatory fines are covered only where they are insurable under the governing law, and that varies by jurisdiction. A Jones Day analysis of fines and penalties coverage explains that there is no uniform view. Some policies use the law of the place that imposed the fine. Others use the venue "that most favors coverage". The Chubb specimen takes the second approach for damages and also excludes fines "not insurable by law". Jones Day adds that defense and investigation costs are not subject to the same insurability question, which is why regulatory defense cover still has value when the fine itself is not covered.
Notification costs are more predictable. In California, Civil Code section 1798.82 requires a business to notify any California resident whose unencrypted personal information was, or is reasonably believed to have been, acquired by an unauthorized person. If more than 500 residents are affected by one breach, a sample notice goes to the Attorney General. For a Los Angeles business with clients across the state, that is the first-party notification line in action. Regulated offices carry extra exposure, which is why we wrote a separate guide on how insurance agencies protect client data.
What to check in a cyber policy before you buy
Take this list to your broker and get written answers. The first four rows come from the FTC and NAIC guidance. The rest come from the exclusions and terms above.
| Question to ask | Why it matters |
|---|---|
| Does it cover first-party and third-party losses? | Many small policies are weighted to one side |
| Does it cover attacks on your data held by vendors, attacks anywhere in the world, and terrorism? | The FTC lists all three as coverage to look for |
| Is there duty to defend wording? | The insurer then manages and funds your defense |
| Is there a breach hotline open around the clock? | Incidents rarely start at 9 a.m. on a Monday |
| Are defense costs inside the limit? | Legal fees can use up the money for settlements |
| Which coverages have sublimits, and how large? | Ransomware, social engineering and fines are often capped |
| What are the retention, coinsurance and waiting period? | Together they set what you pay out of pocket |
| What is the retroactive date and prior knowledge wording? | Old intrusions found later may be excluded |
| How does the war or state-backed attack exclusion decide attribution? | Lloyd's requires the clause to set this out |
| Is betterment or bricking covered? | Upgrades and dead hardware are often excluded |
| Is this a standalone policy or an endorsement? | Endorsements are 55.1% of policies but only 4% of premium |
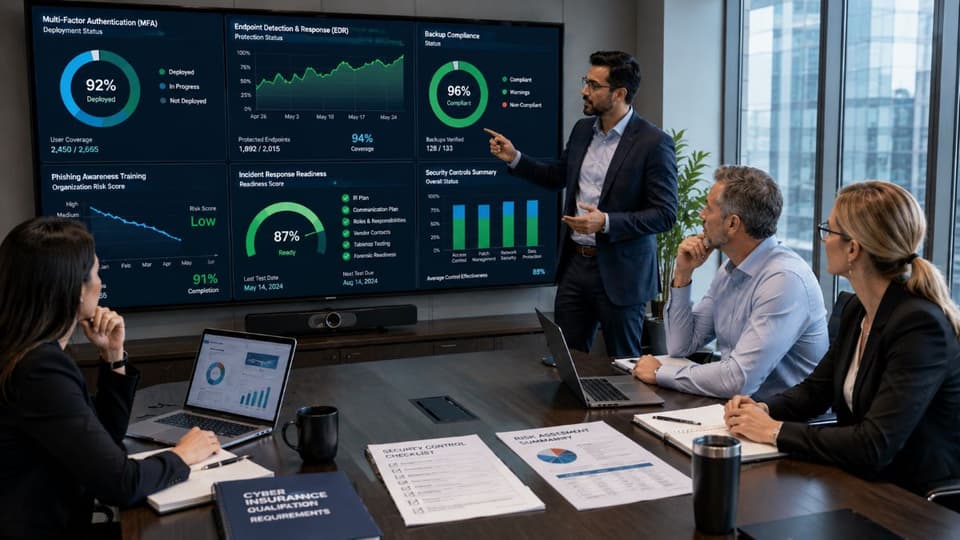
Then make sure your application answers are true on the day you sign and stay true all year. Insurers rely on them, and a wrong answer can undo the whole policy. A quick way to see where you stand is our free security score check, which flags the gaps underwriters ask about most.
How GlobeVM helps with the controls insurers check
GlobeVM does not sell insurance or interpret policy wording. Your broker and a coverage lawyer do that. Our job is the part insurers measure. Every client plan includes firewall management, endpoint protection, email filtering and multi-factor authentication, and we respond within 15 minutes around the clock. We keep dated records of those controls, so you can back up your application answers if an insurer asks. For the full set of controls, see our cybersecurity solutions.
Write your insurer's claim steps into your incident response plan now, while things are calm. The hotline number, the panel vendors and the notice deadline belong on the same page as your IT contacts.
Key sources for this guide are the NAIC and FTC cyber insurance guidance, the NAIC 2025 market report, Lloyd's Market Bulletin Y5381, the FBI's 2024 IC3 report and OFAC's ransomware advisory, all linked above. GlobeVM supports businesses from Los Angeles, CA. Call (818) 405-9930 if you want help getting your controls and records ready before renewal.