Penetration testing cost for a small or mid-sized business usually runs from the mid-four figures into the low five figures. Scope, not a price list, decides where your quote falls. Price guides published in 2026 by U.S. testing firms put most focused engagements between roughly $5,000 and $30,000. A basic external test sits near the bottom, and internal or multi-application work sits near the top.
Preparing for a HIPAA Audit: What OCR Looks For and How to Be Ready

By George
10 October 2026

What you are really buying is a number of skilled tester-days, and every scoping decision adds or removes days. This guide explains what drives a quote, the ranges firms publish for each test, when a regulation makes testing mandatory, and how to avoid paying for a scan dressed up as a test. It is written for the owner or office manager who approves the invoice, not for the tester.
What You Are Paying For in a Penetration Test
A penetration test is a controlled attack by a skilled person who tries to break in, chain weaknesses together, and show what an attacker could reach. That human work separates it from an automated scan, which lists known weaknesses without proving which ones matter. It is also why the two are priced so differently. If you are still sorting out the difference between a pen test and a vulnerability scan, settle that first, because the rest of this pricing only applies to the manual kind.
Most firms price by tester time. Some quote a day rate, and publicly quoted rates run from roughly $1,000 to $3,000 per tester-day. Others quote a fixed fee that still maps back to an estimated number of days. Either way, the size and complexity of what you ask them to test set the pen test cost.
Typical Penetration Testing Cost by Test Type
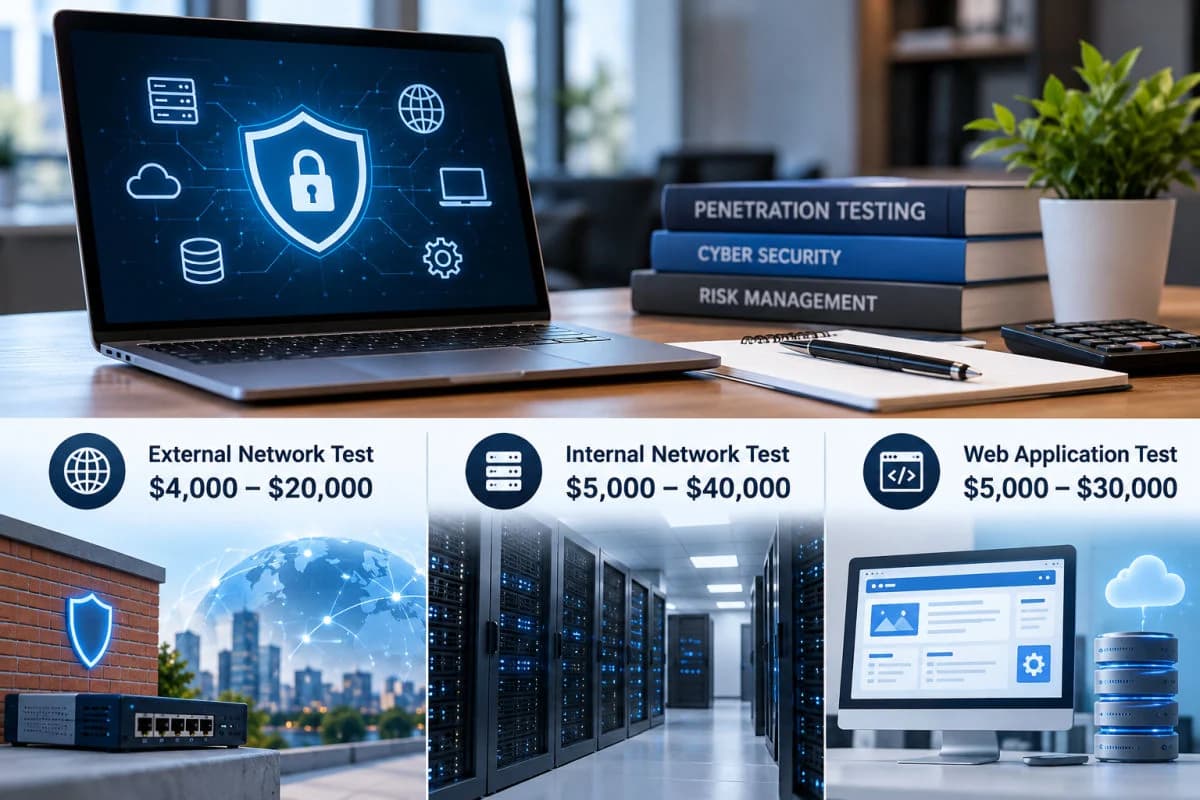
The ranges below come from the same published 2026 pricing guides. They are market ranges, not quotes, and your price depends on how much of each environment is in scope:
- External network test: about $4,000 to $20,000 for internet-facing systems such as firewalls, VPN gateways, email servers, and public websites.
- Internal network test: about $5,000 to $40,000, testing what an attacker could do from inside the network, including against Active Directory.
- Web application test: about $5,000 to $30,000, driven mostly by the number of user roles, pages, workflows, and API endpoints.
For a full year, one published guide puts a typical small-business testing budget at $8,000 to $20,000 for companies of up to about 150 employees. That budget typically covers an annual external test and a test of one or two critical applications. Internal testing gets added as the business grows or as compliance requires it.
Why Quotes for the Same Test Differ
Two quotes for an external test can be thousands of dollars apart, and both can be honest. One firm may plan several days of manual work by a senior tester, include a retest after your fixes, and write a report your auditor will accept. Another may plan a shorter engagement with more automation and bill the retest separately. Penetration testing pricing only makes sense once you compare what each proposal includes, not just the totals.
The Scoping Decisions That Move Your Quote
Every quote starts with a scoping call or questionnaire, and the answers decide the price. These are the variables that move it most:
- Number of IP addresses and live systems in scope for network testing.
- Number of applications, user roles, and API endpoints for application testing.
- How much the testers are told before they start, from nothing at all to credentials and documentation.
- Testing windows, since after-hours or weekend testing to protect production systems costs more.
- On-site or remote, because many internal tests can run through a small device or secure connection instead of a visit.
- Retesting, which some firms include and others bill as a separate engagement.
- Compliance reporting, such as a report formatted for a PCI assessor, which adds documentation time.
The third item deserves the most attention. In gray box testing, the testers receive some credentials and documentation up front. They usually find more in fewer days than testers who start blind, which can lower the cost of a given amount of coverage.
The Costs That Are Not on the Invoice
The quote covers the testers, not your side of the work. Before testing, someone has to answer the scoping questions, create test accounts for each user role, and confirm which systems are in bounds and when. During the test, someone should be reachable to answer questions and to flag any system that starts behaving oddly.
The largest hidden cost comes after the report. Fixing findings takes staff or provider time, sometimes new hardware or licenses, and occasionally a vendor update you have to wait for. Budget for remediation alongside the test itself, instead of discovering that cost when the report lands.
One-Time Projects and Testing Subscriptions
Many small businesses buy testing as an annual project with a fixed scope. Some firms also sell testing as an ongoing subscription, often called penetration testing as a service, which spreads testing across the year and suits companies that release software every few weeks. For an office whose systems change a few times a year, an annual project with a retest is usually the better value.
When a Penetration Test Is Required
For many small businesses, the first quote request is triggered by a rule, a client, or an insurer, not by curiosity. Knowing exactly what each rule asks for keeps you from buying more testing than you need, or less.
PCI DSS for Businesses That Take Cards
PCI DSS 4.0.1 Requirement 11.4 calls for internal and external penetration testing at least once every 12 months and after any significant infrastructure or application change. The tester can be a qualified internal resource or an outside firm, but must be organizationally independent. Exploitable findings must be fixed and the test repeated to confirm the fix. Businesses that use network segmentation to shrink their PCI scope must also test that segmentation, at least annually for merchants and every six months for service providers.
Two details save money here. The quarterly scans PCI requires are vulnerability scans, not penetration tests, so they do not satisfy Requirement 11.4 on their own. Whether your business must meet 11.4 at all depends on how you validate compliance, which is worth confirming against the full PCI DSS 4.0 requirements before you buy a test.
The FTC Safeguards Rule for Financial Businesses
Tax preparation firms, mortgage brokers, and other businesses covered by the FTC Safeguards Rule have two options. They must either run continuous monitoring of their systems or perform annual penetration testing plus vulnerability assessments at least every six months. For a small firm without a monitored security stack, the annual test is usually the practical path.
HIPAA for Medical and Dental Practices
The HIPAA Security Rule in effect today does not use the words "penetration test." It does require a risk analysis and periodic technical evaluations of your safeguards. A penetration test is one of the clearest ways to show that evaluation happened.
That may change. HHS has proposed updating the HIPAA Security Rule to require vulnerability scanning at least every six months and penetration testing at least every 12 months. The proposal is not final, and HHS currently lists July 2027 as the projected date for final action. Practices that test now will not be scrambling if it becomes law.
What a Good Penetration Test Report Includes
The report is the product you keep, so judge proposals partly by a sample report. A useful one contains these parts:
- An executive summary that an owner can read in five minutes.
- The scope, dates, and methodology, such as PTES, OWASP, or NIST SP 800-115.
- Findings ranked by severity, each with evidence showing how it was exploited.
- The business impact of each finding in plain language.
- Specific remediation steps your IT team or provider can follow.
- Retest results or a letter confirming which findings were fixed.
That last item has value outside the security team. The security questionnaires clients send often ask for the date of your most recent test and a summary of the results. A clean retest letter answers the question without sharing the full report.
How to Spot a Scan Sold as a Pen Test
The cheapest offers are usually a different product. Several 2026 price guides warn that a network or web application test priced below roughly $2,000 to $3,000 is almost always an automated scan with a cover page. Watch for these signs:
- No scoping call, or a price quoted before anyone asks what you have.
- No named tester and no description of the tester's experience or certifications.
- Results promised within a day or two of starting.
- A report that reads like tool output, with no exploitation evidence.
- No retest and no explanation of how findings were confirmed.
Scans have real value, and you should run them regularly. They answer a different question from a penetration test, though, and paying test prices for scan output leaves the real attack paths untested.
How to Get More From Your Testing Budget
The fastest way to waste testing days is to let testers spend them finding missing patches you could have found yourself. Run authenticated vulnerability scans and fix what they find before the engagement, which is what a working vulnerability management program does every month. The testers can then spend their time on attack paths only a person can find.
Scope by risk rather than by everything you own. Start with internet-facing systems and the applications that hold sensitive data, and combine external and internal testing in one engagement when you need both. Time the test after a major change, such as a new firewall, a cloud migration, or a new client portal, instead of just before it.
Plan the time after the report as carefully as the test itself. Book the remediation work and the retest date before testing starts, because findings without a deadline tend to sit in a backlog until the next test finds them again. A provider offering penetration testing services should walk you through that whole cycle in the first conversation.
Budgeting for Penetration Testing Cost Year to Year
For many small businesses, penetration testing cost settles into a predictable annual line. That line covers one external test a year, internal and application testing as risk and compliance require, and a retest after every round of fixes. The first year tends to produce the longest list of fixes, and later rounds run more smoothly as the environment improves. Treating testing as a yearly cycle is what turns the report into lasting protection.
Local knowledge helps when a test involves on-site work or coordination with your existing IT provider. For companies in Santa Clarita and across northern Los Angeles County, one team can handle scoping, testing, and remediation in an environment it already knows.
Frequently Asked Questions
Most focused engagements fall between roughly $5,000 and $30,000, based on price guides published by U.S. testing firms in 2026. A basic external network test sits at the low end. Internal network and web application tests with many user roles sit higher, and the final penetration test cost depends on how many systems, applications, and users are in scope.
Firms plan different amounts of manual testing, assign testers with different experience, and include different deliverables. Retesting, compliance-ready reporting, and after-hours testing are common differences, so compare what each proposal includes before comparing prices.
A vulnerability scan costs far less because it is automated, and it is useful for finding known weaknesses on a regular schedule. It does not prove which weaknesses an attacker could exploit or chain together. It therefore does not replace a penetration test when a rule, client, or insurer asks for one.
At least once a year, and after significant changes to your network or applications. PCI DSS requires that cadence for businesses in scope, and the FTC Safeguards Rule requires annual testing for covered financial businesses without continuous monitoring. The proposed HIPAA update would add annual testing for healthcare organizations.
The current HIPAA Security Rule does not name penetration testing, but it requires a risk analysis and periodic technical evaluations, which a penetration test supports. HHS has proposed requiring penetration testing at least every 12 months, but the proposal is not final, and final action is currently projected for July 2027.
Usually not. According to several published price guides, tests priced below roughly $2,000 to $3,000 are almost always automated scans with a cover page. If a low quote comes without a scoping call, a named tester, and exploitation evidence in the sample report, treat it as a scan.
If you want a penetration testing cost estimate built from your actual scope rather than a price list, GlobeVM can scope the test with you and show which systems belong in it.
Comments
0 Comments