Is Zoom HIPAA compliant? It can be, but only when three things are true at once. Your practice is on a paid Zoom plan that Zoom covers with a business associate agreement (BAA), someone at the practice has executed that agreement, and the account is set up and used to protect patient information. The free version never qualifies, and missing any one of the three makes the visit non-compliant, no matter how private it feels.
Keeping the Office Online: A Practical Guide to Business Internet Backup

By George
11 October 2026

The question matters more now than it did in 2021, when many therapists, physicians, and dentists moved to video under temporary pandemic rules and never revisited the setup. This guide draws on our work in IT and cybersecurity for healthcare practices. It explains what changed, how to get a Zoom BAA, what it covers, the settings that protect each session, and how Zoom compares with other HIPAA-compliant video conferencing options.
Is Zoom HIPAA Compliant? The Short Answer
No software is HIPAA compliant on its own. HIPAA applies to your practice and to the vendors that handle patient information for you. Compliance therefore comes from a signed agreement, a platform with the right safeguards, and a practice that uses it correctly. Zoom supplies the first two on an eligible paid plan with a BAA, and the third is your responsibility.
In practical terms, a HIPAA-compliant Zoom setup has three traits. The BAA covers the account every clinician uses, the privacy settings are locked at the account level, and staff follow a short set of rules for recordings, chat, and AI features. Practices running sessions on personal or free accounts are exposed, however careful each clinician is.
Why the Rules Changed After the Pandemic
In March 2020, the HHS Office for Civil Rights said it would not penalize providers for using everyday video apps for telehealth in good faith, even without a BAA. The only condition was that the apps not be public facing. That enforcement discretion expired with the COVID-19 public health emergency on May 11, 2023, and OCR's 90-day transition period ended on August 9, 2023. Since then, providers are expected to use telehealth platforms from vendors that will sign a BAA.
That is why consumer apps such as FaceTime no longer fit patient visits: they do not come with a business associate agreement. Practices that adopted a patchwork of video tools in 2020 should confirm that every clinician has moved to a covered platform. The old habit of sending a personal video link still shows up in plenty of offices.
How to Get a Zoom BAA
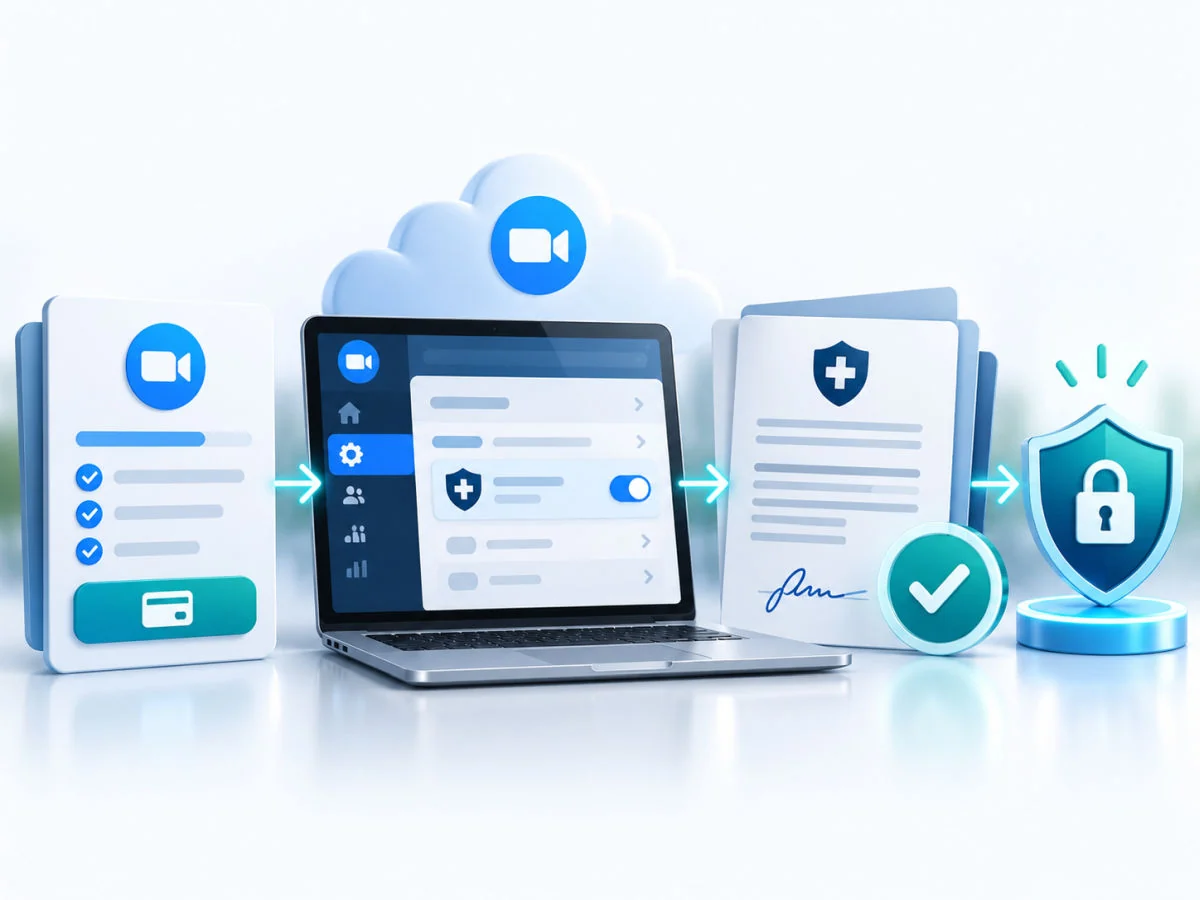
Zoom signs BAAs with healthcare customers. Its support documentation currently lists Pro, Business, Business Plus, and Enterprise plans under Zoom for Healthcare, and Zoom also enters into BAAs with customers on its other paid plans. The path depends on your plan:
- Buying a Pro plan: choose the plan from Zoom's healthcare pricing page and select the United States Agreement (BAA) option during checkout.
- Buying Business, Business Plus, or Enterprise: contact Zoom's sales team to execute the BAA.
- Already on a paid plan: an account administrator can enable the Business Associate Agreement from Plan Management in the Zoom web portal.
Zoom notes that no extra configuration is needed to activate the agreement once it is executed. The agreement and your session settings are still separate things, though. Save a copy of the executed BAA with your other vendor agreements, and if anyone is unsure what a BAA is and why it matters, settle that before the next visit.
Free and Personal Accounts Fall Outside the Agreement
Zoom's BAA process runs through paid plans, so a free account is never an option for patient sessions. The bigger risk in small practices is subtler: a clinician running visits on a personal Zoom account that the practice's BAA does not cover. Move every clinician onto the practice account, stop using personal accounts for patient work, and make that a written rule.
What Zoom's Agreement Covers, and Where to Be Careful
Zoom states that it supports HIPAA compliance programs by executing BAAs and safeguarding protected health information. It says it aligns its controls to the HITRUST Common Security Framework and makes a SOC 2 plus HITRUST report available, which is useful evidence for the vendor review in your risk analysis. The agreement covers Zoom's own services on your account, and the gray areas sit at the edges.
AI Features, Transcripts, and Summaries
Zoom says its AI features, including ZoomMate features, are available to customers with a BAA, with administrator controls to manage them. It also says certain AI features may not be available to healthcare customers under a BAA. Zoom states that it does not use customers' audio, video, chat, or other meeting content to train its own or third-party AI models. The open decision for your practice is whether to turn these features on, because transcripts and summaries create new records of patient information.
Those records need access limits and a retention rule of their own. Third-party AI note-takers are a separate matter: a bot from another company that joins the session is a vendor Zoom's agreement does not cover. It needs its own BAA, or it should be blocked, the same question practices face when they ask whether ChatGPT is HIPAA compliant for clinical notes.
Marketplace Apps and Integrations
Many apps in the Zoom App Marketplace are built by other companies, even when they appear inside the Zoom window. Any app that can see meeting content, chat, or recordings needs its own review, and its own BAA if it touches patient information. Restrict app installation to administrators so a well-meaning staff member cannot connect one alone.
The Zoom Settings That Protect Each Session
Set these at the account level and lock them, so individual users cannot loosen them for convenience. The goal is a visit that only the patient can join, that leaves no records you did not intend to keep, and that nobody can quietly share:
- Waiting room on for every meeting, with patients admitted one at a time.
- A unique link or meeting ID for each visit, not a reused personal meeting room where the next patient could arrive early.
- Passcodes required, and multifactor authentication or single sign-on for every staff account.
- Screen sharing limited to the host, so a participant cannot take over the screen.
- Cloud recording off by default, turned on only for documented reasons.
- Chat file transfer restricted, and chat saving settings chosen deliberately.
- Automatic updates enabled, since outdated clients miss security fixes.
Zoom also offers optional end-to-end encryption for meetings. It adds protection, but turning it on disables some features, including cloud recording. Decide which sessions need it, rather than switching it on everywhere and discovering the trade-offs mid-visit.
Recording Sessions
HIPAA does not ban recording, but a recorded visit is protected health information that must be stored, accessed, and eventually deleted under your policies. California also requires consent from all parties before a confidential communication is recorded. A recorded session therefore needs a consent step every time, not a line buried in intake paperwork, and for most therapy practices the simplest answer is not to record at all.
If something goes wrong, such as an uninvited person joining a session or a recording shared with the wrong person, treat it as a possible breach and assess it promptly. The HIPAA breach notification rule sets out how to evaluate the incident and who must be told.
Zoom Compared With Other HIPAA-Compliant Video Conferencing Options
Zoom is one of several routes to compliant video visits, and the right choice usually follows the tools your practice already runs. Microsoft Teams falls under Microsoft's business associate agreement for practices on Microsoft 365. Google Meet is covered under Google Workspace's BAA once an administrator accepts it. Purpose-built telehealth platforms and the video tools inside many electronic health record systems are also options, often with scheduling and intake included.
The same three tests apply to every one of them: an eligible plan, an executed agreement, and settings that hold. Practices that follow up on visits by text should apply those tests there too, since HIPAA-compliant texting has its own rules for reminders and patient choice.
When the Video Drops and the Visit Moves to Audio
Video visits fail, and many of them finish by phone. HHS guidance from June 2022 says audio-only telehealth over a traditional landline is not subject to the Security Rule, because nothing is transmitted electronically. Calls through apps, internet phone systems, or cellular and Wi-Fi connections are covered by it. A vendor that only carries the call is treated as a conduit, but one that stores recordings, voicemails, or transcripts for you needs a BAA.
The same guidance asks providers to hold audio-only visits from a private setting, or with lowered voices and no speakerphone when privacy is not possible. Providers should also verify the identity of patients they do not already know. Build that fallback into the visit script so switching to audio does not become the weakest part of the session.
A Practice Checklist Before the Next Video Visit
Work through this list once, then review it whenever you change plans, add clinicians, or turn on new features. Assign one person to own it so it does not drift:
- Confirm that your Zoom plan is eligible and that the BAA is executed and on file.
- Move every clinician onto the practice account and retire personal accounts for patient work.
- Lock waiting rooms, passcodes, host-only sharing, and recording defaults at the account level.
- Decide which AI features are allowed, and block third-party note-taking bots without a BAA.
- Review every connected Marketplace app and remove the ones you cannot vouch for.
- Write a recording rule with a consent script, or a rule that sessions are never recorded.
- Give patients simple instructions for joining from a private place.
- Add Zoom to your risk analysis and your vendor inventory.
Staff need a short walk-through of the rules, because most telehealth problems start with a shortcut rather than a software flaw. Include the video platform in your annual training so it meets the HIPAA training requirements you already track.
Keeping Telehealth Compliant as Zoom Changes
Zoom adds features constantly, and each new capability reopens the question of what data it creates and where that data goes. AI, recording, and integration features deserve the closest look. So is Zoom HIPAA compliant for your practice over the long run? That depends on keeping the agreement, the settings, and the habits aligned as the product evolves.
For practices that want a second set of eyes, a HIPAA risk review can cover the video platform alongside email, phones, and the rest of the patient-facing stack. Record the results with the rest of your risk analysis so the evidence lives in one place.
The quarterly check itself does not need to be elaborate. Confirm the agreement is still in force and the locked settings have not changed. Then look at which features and apps were added since the last review, and you will catch most problems while they are still small.
Local support helps when a clinician's laptop, camera, or connection fails minutes before a session. For medical and therapy practices around Thousand Oaks, that means someone who can fix the problem the same day instead of rescheduling the patient.
Frequently Asked Questions
Yes, when the practice is on an eligible paid Zoom plan, has executed Zoom's business associate agreement, and configures the account to protect each session. Therapists should pay particular attention to waiting rooms, unique meeting links, recording rules, and AI features, since therapy notes and recordings are especially sensitive.
No. Zoom's business associate agreement is available on paid plans, so free accounts should never be used for sessions that involve patient information. Personal accounts held by individual clinicians should also move under the practice's covered account.
With a Pro plan, select the United States BAA option at checkout on Zoom's healthcare pricing page. For Business, Business Plus, or Enterprise plans, contact Zoom's sales team. If you already have a paid plan, an administrator can enable the BAA from Plan Management in the web portal.
Not for patient visits. FaceTime was tolerated during the COVID-19 public health emergency, but that enforcement discretion ended in 2023, and consumer apps like FaceTime do not come with a business associate agreement. Use a telehealth platform whose vendor signs a BAA.
Zoom says its AI features are available to customers with a BAA, though some may not be available to healthcare customers. Transcripts and summaries become patient records, so decide deliberately which features to allow. Restrict access to their output and set a retention rule before turning them on.
In California, yes. State law requires consent from all parties before a confidential communication is recorded, and any recording is protected health information that must be secured and retained under your policies. Many practices avoid the issue entirely by not recording visits.
If you want to confirm that your video visits meet HIPAA before the next patient logs in, GlobeVM can review your Zoom setup and the rest of your telehealth workflow with you.
Comments
0 Comments